PHP2Shell: one request takes over PHP
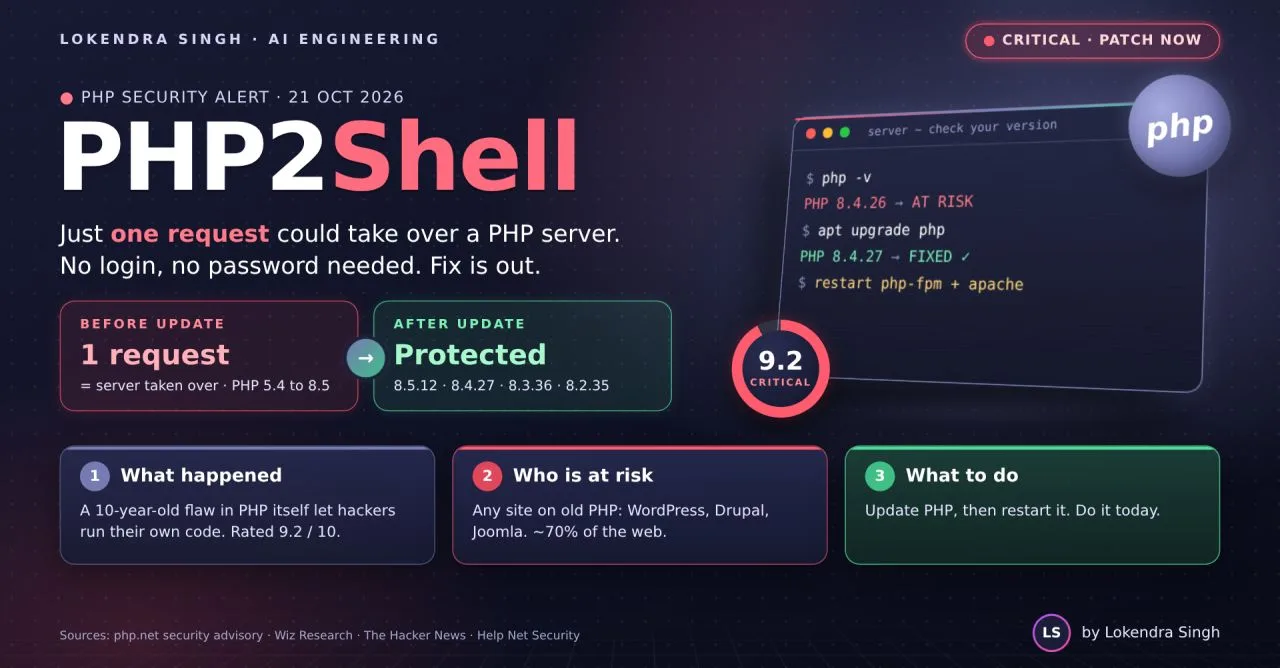
Just one request could take over a PHP server. No login. No password. Meet PHP2Shell.
What happened
- A 10-year-old flaw inside PHP itself (since PHP 5.4)
- 2 bugs, CVE-2026-109618 + CVE-2026-109619, rated 9.2 / 10
- Hackers could run their own code on your server
- Found by Wiz, Calif and OpenAI, with help from AI
Who is at risk
- Any site on old PHP: WordPress, Drupal, Joomla and more
- PHP runs ~70% of the web
- Even a simple "Hello World" page, because the bug is in PHP, not your code
What to do
- Update to 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35
- Restart PHP-FPM, Apache and all workers
- On 8.1 or older? Upgrade, or ask your vendor for a backport
php -v                 # PHP 8.4.26 = at risk
sudo apt upgrade php   # PHP 8.4.27 = fixed
sudo systemctl restart php8.4-fpm apache2
Honestly
- Attack attempts were already seen before the fix went public
- Config tweaks only lower risk. Only the update fully fixes it
My take
AI is now finding decade-old holes in days. Your patch speed matters more than ever.
Run php -v today. Are you patched?
Sources
- php.net - PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 released (21 Oct 2026)
- Wiz Research - CVE-2026-109618
- The Hacker News and Help Net Security (21 Oct 2026)